Business Security and Privacy for Oakville
Oakville's professional offices and head offices hold client data that deserves careful protection. An audit backed by evidence, followed by a hardening project quoted in writing, shows exactly where you stand and what to fix first. I work remote first and come to Oakville for staff training by arrangement.
Find the weak points before someone else does, fix them to a written quote and keep them fixed.
Most breaches at small businesses are automated and opportunistic. An unpatched plugin, a password reused from a leaked site, an exposed admin port. A short audit surfaces them with evidence, a hardening project closes them, and ongoing monitoring keeps them closed.
Services
Security Audit
External and internal review of your servers, sites, accounts and access. An action list on a single page, prioritized findings with evidence and a written quote for the fixes. Half the fee is credited against the first fixes if I take the systems on.
Book an auditIncident response
Something is wrong right now: a defaced site, a locked account, strange traffic, a ransom note. Contain, investigate, restore and write up what happened and what to change.
Get help nowHardening project
- Two step sign in and passkeys
- Role based access
- Audit trails
- Content Security Policy and web hardening
- Container hardening
- Vulnerability scanning in your deploy pipeline
Ransomware resistant backups
Encrypted backups to a second location that an attacker on your network cannot reach, delete or encrypt, with retention so last week's clean copy still exists and restores rehearsed on a schedule, so recovery takes a known number of hours.
Ask about backupsStaff training and password management
A short session for your team on phishing, passwords, two step sign in and what to do when something looks wrong, plus a password manager rolled out and configured for the business, with shared vaults and offboarding built in.
Book a sessionCertificate and TLS automation
Certificates that renew themselves, long before anyone notices a date. Automated issuance, renewal and monitoring across every host and service, with alerts long before anything expires.
Jobs are quoted in writing after a free scope, so you know the number before any work starts.
Audits with evidence behind every finding
You see what I saw
Every finding comes with the command, the screenshot or the log line that proves it, an explanation of why it matters written for a non technical reader and a priority. The report opens with an action list on a single page and comes with a written quote for the fixes.
The audit runs from a read only evidence collector I built, so nothing on your servers is changed while I look. It covers the operating system, the services, the web stack, the accounts and the network edge in one pass, and the same collector runs again after the fixes so you can see each finding close. Patching is check, patch and recheck, and customer servers are only touched after you approve the plan.
Part of every audit is an access review: who still holds a login, an API key, a server key or a firewall allowance and whether they should. Staff and contractors who have moved on are the most common gap. Their access tends to outlive them, sometimes with the business phones or the deploy pipeline still depending on it, and that is exactly what an attacker or a disgruntled leaver uses. I find those accounts, work out what depends on them and close them cleanly.
Attack forensics and hardening in response
When someone is already knocking
I have investigated sustained attack campaigns against client sites: reading the logs, reconstructing what the attacker tried, confirming whether anything got through and closing every weakness they probed. You get a written report, with the evidence, that says what happened and what changed.
Then the edge gets hardened so the next campaign bounces. In practice that is web security in front of the site with tools such as Cloudflare, rate limits and bot rules tuned to your real traffic, origin servers that only answer to the edge and login and admin paths locked down.
After that, vulnerability scanning on a schedule and automatic detection of newly disclosed vulnerabilities that affect your stack, so exposure is patched quickly instead of lingering for months until someone finds it.
Hardening that stays hardened
Built into the pipeline from the start
Two step sign in and passkeys, role based access, audit trails and a Content Security Policy close the common doors. Vulnerability scanning in the deploy pipeline stops new ones opening. Containers run with least privilege.
This is the same discipline I apply at enterprise scale in DevSecOps, scoped to what a small business runs.
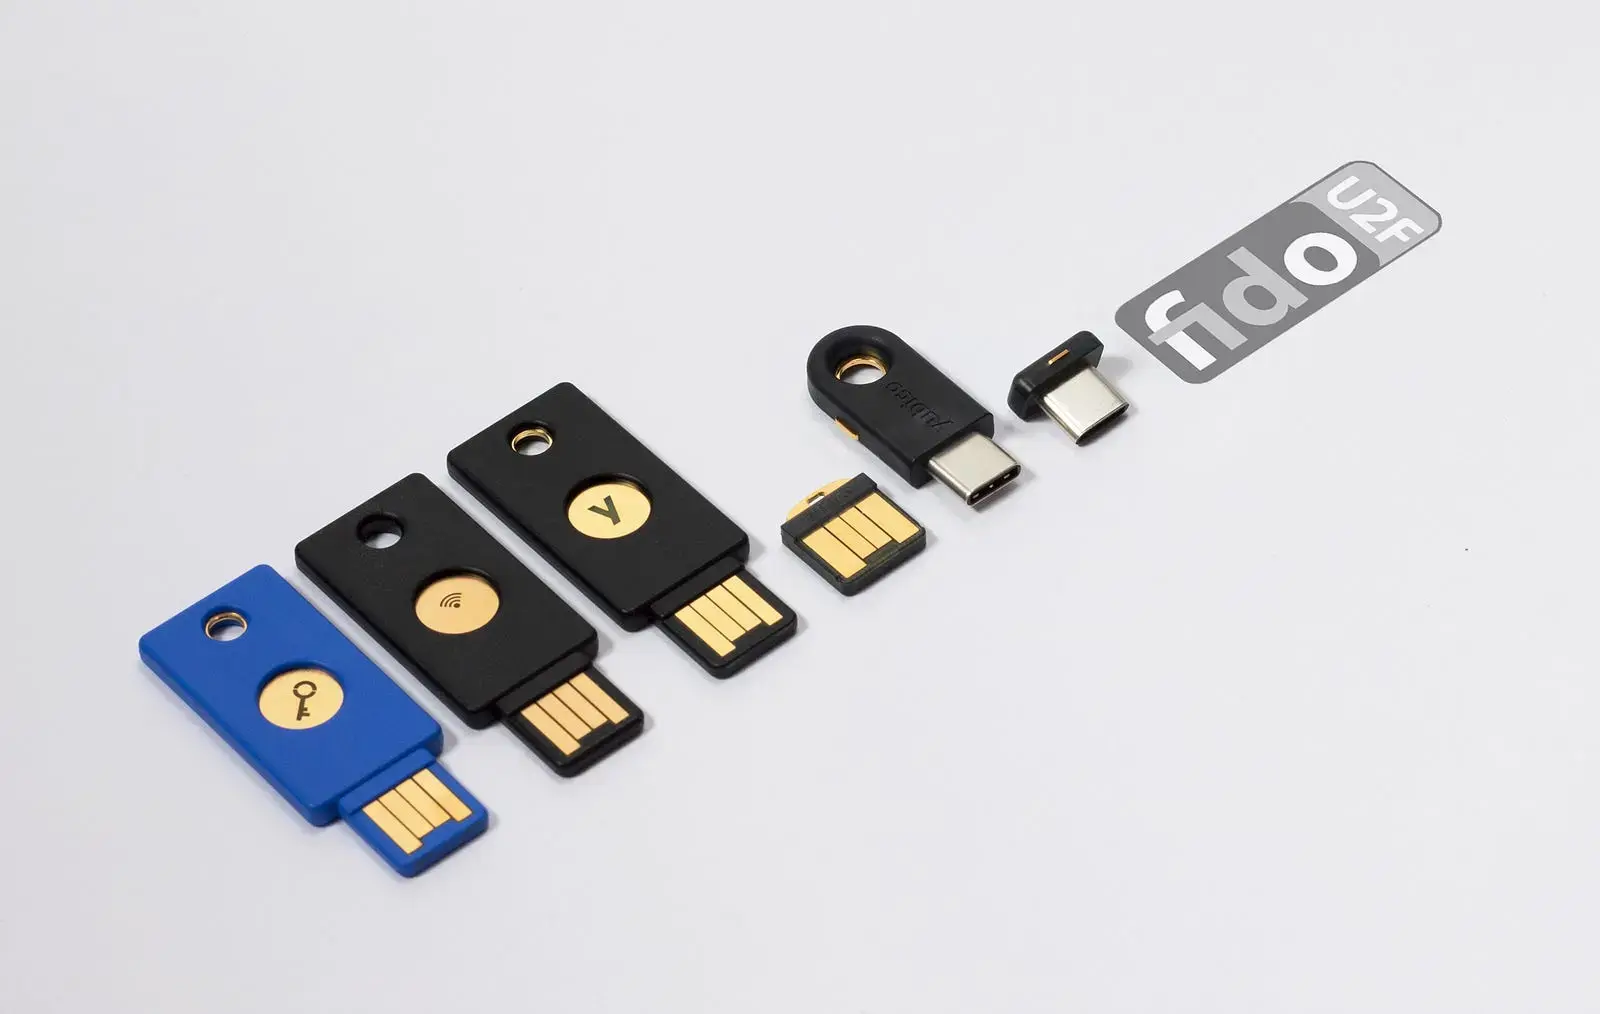
Remote staff and contractors get in without your network being open to the world. Encrypted tunnels, hardware keys and access for each person that can be revoked in a minute replace shared passwords and open ports.
Backups that survive ransomware, and people who know the drill
The two controls that decide whether an incident is a bad day or the end of the business
Ransomware works because the backups are on the same network as everything else, so they get encrypted too. I set up backups that go somewhere the attacker cannot follow. They are encrypted and copied off site, some copies cannot be altered or deleted for a set period, and old versions are kept so a clean copy from before the infection still exists. Then I restore from them on a schedule and report the result, because a backup that has never been restored is only a guess.
Most incidents still start with a person, through a convincing email, a reused password or a login with no second factor. I run short, practical training sessions for staff, roll out a password manager so no one has to remember or reuse anything and add two step sign in or passkeys to the systems that matter, including the apps and services I build and maintain. When someone leaves, their access goes with them, in one place.
Most incidents still start with a person, through a convincing email, a reused password or a login with no second factor. I run short, practical training sessions for staff, roll out a password manager so no one has to remember or reuse anything and add two step sign in or passkeys to the systems that matter, including the apps and services I build and maintain. When someone leaves, their access goes with them, in one place.
What changes after the work
- Findings with evidence, priorities and an action list on a single page
- An access review that finds and closes leftover accounts, keys and firewall holes
- Two step sign in, passkeys and role based access on your systems
- Encrypted, off site backups that cannot be altered for a set period, with rehearsed restores
- Staff trained in a short session, with a password manager rolled out for the business
- Edge protection, rate limits and bot rules in front of your site
- Certificates that renew themselves and alert before expiry
- Vulnerability scanning on every deploy and alerts for newly disclosed exposure
Individuals
Looking for help with your own devices, home network or phone? See personal privacy and security.
Security questions
- Yes, one product. If I take the systems on afterwards, half the audit fee is credited against the first fixes.
Audits and incidents I have handled
Creating my own start-up company I was hesitant and didn't really think I required the services of Viscous Bits. However, after a consultation I quickly realised it was best to have them help my business handle my IT needs. I now consult Viscous Bits every time I have questions for prompt and helpful service. Having Viscous Bits as my IT Support team makes me feel comfortable knowing my data is safe and secure.
- Secret Lands FarmA farm store that stays safe and keeps sellingA family farm's online store moved to a faster server, kept up to date safely, watched day and night and explained to the owners once a month.Read the case study
- Optima Windows & DoorsFrom ransomware protection to a quoting platformIt began as security consulting to protect a window and door business from ransomware. It became a digital transformation, with a custom quoting tool the sales team opens every morning.Read the case study
- Ostrich Land OntarioEyes on the farm, day and nightA working ostrich farm that is also a visitor attraction. Desktop support first, then a security camera system covering the grounds and the store.Read the case study
Start with a free external security check
One domain, seven checks, a short note sent back encrypted. Ownership proven with a DNS record first.